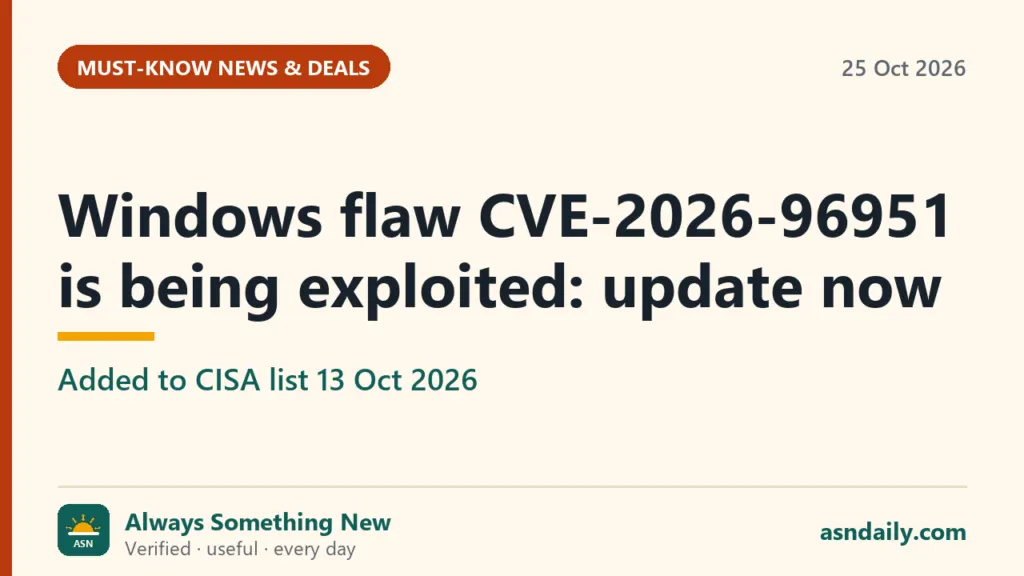
CISA, the US cybersecurity agency, lists a Windows vulnerability, CVE-2026-96951, in its Known Exploited Vulnerabilities catalog. Microsoft released a fix with the October 2026 updates. If your Windows PC has not installed updates since 13 October 2026, open Windows Update today and install them. Last checked: 25 Oct 2026.
What it is
The Known Exploited Vulnerabilities (KEV) catalog is a list kept by CISA. A flaw is added to it when there is evidence that attackers are already using it. The entry for CVE-2026-96951 names Microsoft as the vendor and Windows as the product. CISA’s catalog shows the date it was added as 13 October 2026, with a due date of 16 October 2026. That due date is a deadline for US federal agencies. It does not apply to home users, but it shows how urgently the fix is treated.
We have deliberately kept this post short on technical detail. When we checked, Microsoft’s security page and the NVD entry did not load their content for us, so we cannot confirm the type of flaw, its severity score or the exact update number that fixes it. We will not guess. What we can read on CISA’s page is enough to act on: Windows, exploited, fixed in the October 2026 updates.
Who it is for
This matters to anyone who uses a Windows PC or laptop: students, office workers, shop owners using billing software and families sharing one computer. It matters most if your machine has updates paused, if it is often switched off during update time, or if it is on a slow or metered connection where updates keep failing. If you look after a few computers in a small office, check each one, not just your own.
What to do
- Click Start and open Settings, then Windows Update.
- Click “Check for updates”.
- Let every pending update download and install.
- Restart the PC when asked.
- Open Windows Update again. It should say that you are up to date. If more updates appear, install those too.
- If updates are paused, choose the option to resume updates first.
If an update fails repeatedly, make sure you have enough free disk space and a stable internet connection, then try again. Do not download “patches” from websites, messages or videos. Windows updates come only through Windows Update or Microsoft’s own website.
What to watch out for
News of a security flaw is often used by scammers. Be careful of emails, WhatsApp forwards or phone calls that say your PC is “infected with CVE-2026-96951” and ask you to install a tool or share a code. Real update prompts never ask you for money or for a code over the phone. If you lose money to a scam, call the cybercrime helpline 1930.
Also note what we do not know. We could not read the fixed build number, so we cannot give you a version to compare against. Installing all pending updates and seeing that Windows is up to date is the check to use.
Source and verification
Checked against CISA Known Exploited Vulnerabilities Catalog on 25 Oct 2026. The catalog lists the vendor (Microsoft), the product (Windows), the date added (13 Oct 2026) and the due date (16 Oct 2026) for CVE-2026-96951. We did not publish any detail that we could not read on an official page.
Get one useful update every day
Verified, short, free. Join our Telegram channel: t.me/asn_daily · Instagram: @asn_daily